DORA - Digital Operational Resilience Act
IT inventory

IT inventory
DORA articles: 7, 8, 9, 11, 13, 14, 17, 19, 24, 25, 28, 37, 45
Versio.io offers a fully automated and continuous inventory of the entire IT landscape - including all third-party assets and configuration items. Status changes are seamlessly historised and documented in an audit-proof manner. The mapping of topological relationships creates full transparency and a deep understanding of dependencies and risks.
A central basis for the effective implementation of DORA specifications.
Process monitoring

Process monitoring
DORA articles: 8, 9, 12, 13, 18, 24, 25, 28, 37
The fully automated monitoring and analysis of business processes and batch job processes allows workflows to be controlled efficiently and optimisation potential to be identified at an early stage.
At the same time, automated monitoring of the availability and performance of IT services enables rapid fault detection and seamless documentation - including a financial assessment of potential damage. This ensures holistic, proactive IT and process monitoring.
Change management

Change management
DORA articles: 7, 8, 9, 11, 17, 19, 24, 25, 37
The automated detection of changes to assets and configuration items ensures seamless tracking of system changes. In addition, the analysis of the change history enables a well-founded assessment of effects and risks.
The fully automated monitoring and management of planned measures ensures that changes are controlled, documented and implemented efficiently - for maximum transparency and stability in IT operations.
IT governance

IT governance
DORA articles: 7, 8, 9, 10, 11, 13, 17, 24, 25, 37, 45
By defining internal and regulatory requirements in the form of logical rules, compliance requirements can be verified automatically and potential risks identified at an early stage.
In addition, the evaluation of the product life cycle - particularly in the area of release and patch management - enables the targeted identification of publicly known vulnerabilities (CVE) in hardware and software products in use. This ensures proactive security and risk management across the entire IT portfolio.
Risk management
Risk management
DORA articles: 5, 7, 8, 9, 11, 14, 17, 18, 24, 25, 37, 45
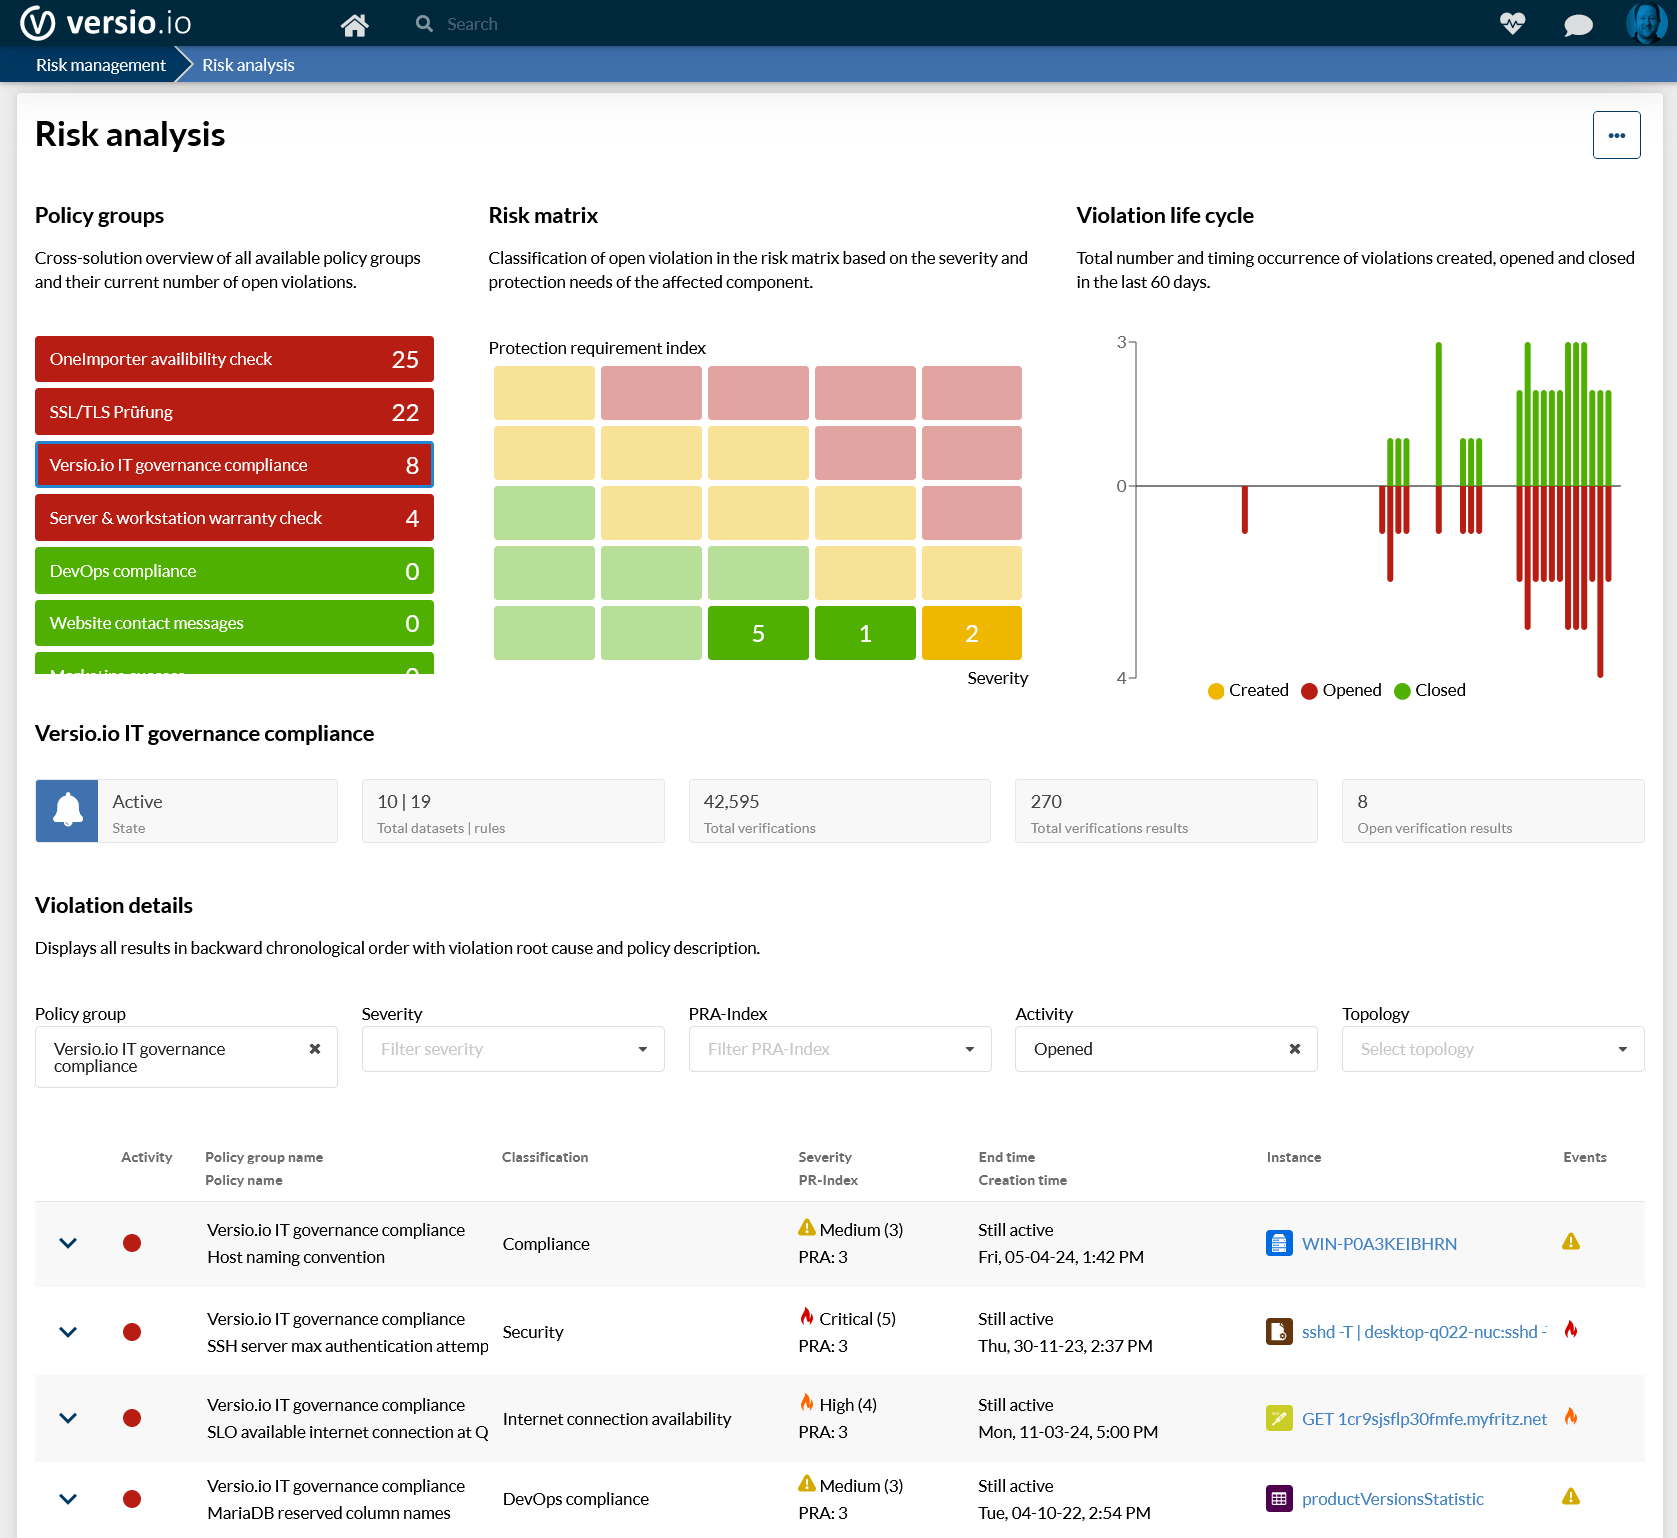
The automated determination of the protection requirements for each asset and configuration item takes into account the criteria of confidentiality, integrity and availability - including a consistent inheritance of the determination of protection requirements. On this basis, risks are classified according to their protection requirements and severity.
In addition, comprehensive risk analysis and risk management functions provide a sound basis for IT risk management decisions.
Authorisation

Authorisation
DORA articles: 5, 8, 9, 17
A clear organizational structure is created through the targeted assignment of inventoried assets, configuration items, guidelines and tasks to defined areas of work and responsibility.
User access and authorisations can be controlled granularly via user groups for each area of responsibility. In addition, filtering views and reports according to work areas enables efficient, role-based provision of information.
Event & Alerting

Event & Alerting
DORA articles: 10, 19
Status changes within IT governance and risk management automatically trigger dedicated events. These enable targeted alerting of users or the connection of external systems.
Notifications can be sent by email or chat, as well as the automated creation of incident and problem tickets. In addition, any third-party systems can be flexibly integrated via generic webhooks.
Digital Operational Resilience Act PDF Download
Read more

NIS2 - Efficient and prompt operational implementation
Meet NIS2 requirements article by article: risk management, incident handling, supply chain security and vulnerability management – automated with Versio.io

ISO 27001 - Efficient operational implementation
ISO 27001 explained: ISMS, CIA triad, certification process – and how Versio.io automates asset inventory, risk and policy monitoring for certification.

CRA - Efficient and prompt operational implementation
The EU Cyber Resilience Act (CRA) explained: SBOM, vulnerability handling, support period and reporting obligations - and how Versio.io supports manufacturers with CRA compliance.
Talk to us