Policy monitoring
Defining internal and regulatory policies and monitoring their compliance to stabilise operations and minimise business risks
In a nutshellRequest demoStart free trial

Define customer-specific policies in order to be able to check internal & legal standards

Define customer-specific policies in order to be able to check internal & legal standards
In Versio.io Policy monitoring, users can define custom policies in an easy-to-use visual policy editor using AND and OR logic. Each change detected by Versio.io can be verified to see if the change in state affects the business risk.
All policies together form an internal repository for knowledge sharing within the team, as well as making it easier for auditors to verify during internal audits or external certifications.
The governance policy template repository helps your team with initial setup

The governance policy template repository helps your team with initial setup
Using Versio.io gives you access to the IT governance knowledge base. Here you will find many predefined IT governance policies, which you can adapt to your individual needs. The policy templates are based on specifications or recommendations from product manufacturers, institutions or the current state of the art.
The knowledge database enables you to implement solid IT governance in a timely manner and thus minimise corporate risks. Furthermore, it represents a first-class knowledge base for your employees.
Fully automated and continuous verification of IT governance compliance
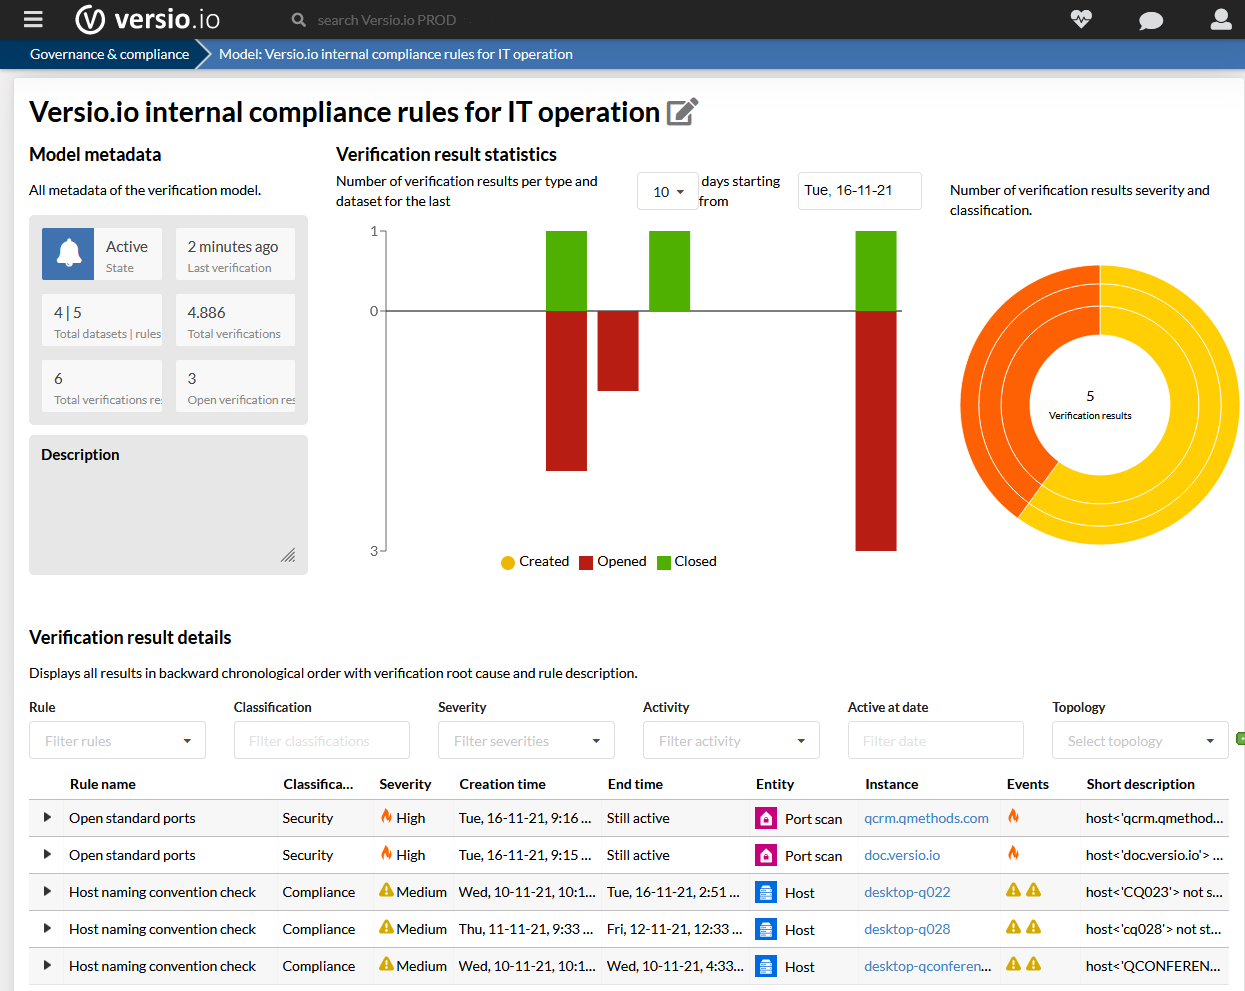
Fully automated and continuous verification of IT governance compliance
Any change detected by the Versio.io Asset and Configuration Item Inventory will have the activated policies applied. Thus, Versio.io alerts you in business real time about violations of internal and external policies.
For each policy violation, the start and end times of the IT governance violation are recorded and stored in an audit-proof manner. This allows the origin of the violations to be fully traced up to their resolution.
Identified violations are followed up with a detailed root cause analysis

Identified violations are followed up with a detailed root cause analysis
For each IT governance breach, events are generated for detection and resolution of the occurrence. The events contain all the necessary information, references and a detailed root cause analysis to be able to capture the cause of the problem in a timely manner.
Any event can trigger an alarm. This means that users are notified of the event via email or chat, that light signals are triggered in offices or that incident tickets are created in ITSM solutions.
Read more

Configuration mgm. database
Audit-proof CMDB with fully automated full-stack inventory: change history, topology, reporting and ServiceNow sync – your single source of truth for IT.

Supported integrations for event-based alerting
Forward Versio.io events to Slack, Microsoft Teams, Mattermost, email, Telegram, ServiceNow, TOPdesk, Jira, GitLab, GitHub, IoT actuators and webhooks.

Automation of BAIT for IT operations
Automate the banking supervisory requirements for IT (BAIT): inventory, change management, backups and incident handling in IT operations with Versio.io.
Talk to us